AI Coding Tools: Can You Really Trust Them?
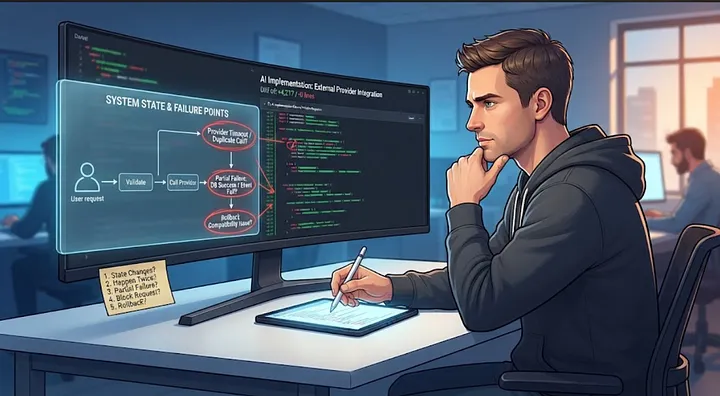
An engineer opens their IDE, types a prompt requesting a user authentication middleware function, and watches as an advanced model instantly streams a clean, well-formatted block of code. The syntax is pristine, variables are named intuitively, and the function even includes helpful comments. When the engineer runs the initial test suite, everything passes on the first try. Yet, buried within the logic is a subtle authorization bypass that fails to validate token expiration correctly under high concurrency—a flaw that goes completely unnoticed until it hits a staging environment.
This scenario captures the central tension facing modern engineering teams: AI coding tools can dramatically accelerate output, but the code they produce can look correct, run successfully, and still harbor critical flaws. For startup founders, CTOs, and engineering leaders, the promise of higher velocity comes hand-in-hand with valid questions about software quality and security. Can you trust AI coding tools, or are organizations trading long-term maintainability for short-term speed gains?
Evaluating this question requires looking past vendor hype to examine what these models actually do well, where they fail, and how engineering teams can implement robust oversight.
What AI Coding Tools Get Right—and Where They Fall Short
Modern AI code generation models are remarkably sophisticated pattern matchers trained on massive corpuses of open-source repositories, documentation, and technical discussions. When deployed correctly, they function as tireless junior assistants that transform the mechanics of daily software engineering.
Where AI Excels
-
Boilerplate and Repetitive Tasks: Generating standard configuration files, repetitive API endpoint scaffolding, or repetitive boilerplate code frees developers from tedious setup work.
-
Documentation and Testing: AI models excel at drafting initial unit test suites, generating docstrings, and explaining complex, unfamiliar legacy codebases.
-
Refactoring and Exploration: Developers can use AI to suggest alternative algorithmic approaches, refactor messy loops, or translate code patterns from one language to another.
-
Prototyping: For early-stage products, accelerating routine feature development helps teams test concepts and validate product hypotheses faster.
Where AI Falls Short
Despite these strengths, AI code generation has structural limitations. Models lack genuine semantic understanding of business intent or system architecture. They operate on probability, predicting the most statistically likely next token based on their training data.
This leads to several recurring failure modes:
-
Incomplete Context: An AI assistant rarely understands the broader architectural constraints, data models, or security policies of a proprietary codebase.
-
Outdated Patterns and Hallucinated APIs: Models frequently suggest deprecated libraries, insecure coding paradigms, or entirely fabricated API methods that look plausible but fail in practice.
-
Superficial Correctness: Because AI-generated code often matches syntactic conventions, it creates a false sense of security. It satisfies the immediate prompt without satisfying hidden edge cases, performance constraints, or non-functional requirements.
Distinguishing between generating code quickly and producing software that is correct, secure, maintainable, and fit for purpose is the fundamental challenge facing engineering organizations today.
The Hidden Risks of AI-Generated Code: Security, Bugs, and Bias
When considering whether AI coding tools security risks should prevent widespread adoption, teams must look beyond theoretical concerns to examine practical vulnerabilities. Risks of AI-generated code manifest in several distinct ways across software projects.
Security Vulnerabilities and Logic Flaws
One of the most persistent concerns is the introduction of insecure coding patterns. Because training data often includes vulnerable code from public repositories, models can replicate common security flaws, such as SQL injection vectors, insecure direct object references, or improper input sanitization.
Illustrative Example: Consider an AI assistant tasked with writing a database search query. It might construct a string concatenation approach that handles normal inputs perfectly, yet fails to sanitize special characters properly. If deployed without review, this creates an immediate vulnerability that a malicious actor can exploit.
Incorrect Business Logic and Edge Cases
AI models do not understand the nuanced rules governing a specific business domain. A generated function might calculate discounts or tax rates using standard formulas while missing company-specific regulatory requirements or exception paths. These logic gaps often bypass automated unit tests if the test suite itself was also co-created by the same AI model, creating a dangerous echo chamber of assumptions.
Dependency and Ecosystem Risks
AI coding tools frequently recommend third-party packages, libraries, or npm modules to solve specific sub-tasks. However, models can suggest abandoned packages, unmaintained libraries, or packages subject to typosquatting attacks. Without rigorous dependency checks, teams inherit supply-chain vulnerabilities.
Privacy, IP, and Maintainability
Submitting proprietary business logic, internal database schemas, or customer data to external AI models can create compliance and confidentiality risks depending on the enterprise agreement in place. Furthermore, long-term maintainability suffers when developers integrate complex code they do not fully understand. If an engineer cannot explain why a particular snippet of AI-generated code was written a certain way, debugging production incidents becomes significantly harder.
Can AI Write Production-Ready Code Without Human Oversight?
To answer the common question: Can AI-generated code be trusted in production environments?—the reality is nuanced. Can you trust AI coding tools blindly in high-stakes environments? Absolutely not. However, treating them as autonomous developers misunderstands their utility.
Production readiness depends heavily on the risk profile of the task at hand:
-
Low-Risk Tasks: Generating utility formatting functions, basic mock data generators, or draft README documentation carries minimal risk. If an error occurs, the blast radius is small.
-
High-Risk Work: Code involving authentication, authorization, cryptographic operations, payment processing, personal identifiable information (PII), or core infrastructure demands rigorous human oversight.
Experienced developers must act as architects and reviewers rather than mere typists. They are responsible for validating underlying assumptions, reviewing implementation choices, understanding system dependencies, and—above all—accepting ultimate accountability for the software released to users. AI-generated code is a draft, never a finished product.
How-To Verify AI-Generated Code Before It Reaches Production
Mitigating the risks of AI-generated code requires a systematic verification framework. Establishing rigorous human code review for AI-generated code ensures that speed does not compromise quality.
An Actionable Verification Framework
-
Define Requirements First: Clearly outline acceptance criteria and expected behavior before prompting an AI tool. Never use AI generation as a substitute for product specification.
-
Inspect Against Architecture: Confirm that the output aligns with existing design patterns, coding standards, and architectural boundaries rather than introducing conflicting paradigms.
-
Conduct Security Scrutiny: Review the implementation for injection vulnerabilities, exposed secrets, improper data handling, and authorization flaws.
-
Execute Comprehensive Testing: Run unit, integration, regression, and stress tests. Pay special attention to edge cases and concurrent execution paths.
-
Utilize Automated Tooling: Integrate static analysis tools, linters, and software composition analysis (SCA) to catch syntax issues, deprecated methods, and vulnerable dependencies automatically.
-
Enforce Strict Review for Sensitive Code: Apply mandatory peer review for any AI-assisted code touching authentication, payments, or core data models.
Practical Review Example: AI-Generated Payment Workflow
The Issue Checked: An AI assistant suggests a Stripe webhook handler that processes payment confirmation events without verifying the cryptographic signature header.
The Validation Step: The reviewing engineer identifies the missing signature verification, rejects the snippet, and enforces the implementation of official security libraries to authenticate incoming webhook payloads before updating database records.
Passing tests and automated scans reduces risk, but it does not guarantee that code is entirely secure or correct. Continuous monitoring and human judgment remain indispensable.
Building a Smarter Development Workflow With AI Coding Tools
Adopting AI coding tools successfully requires organizational discipline. Successful implementation relies on clear governance rather than unrestricted access.
-
Establish Acceptable-Use Policies: Define clear guidelines regarding what data, codebases, and intellectual property can be shared with external AI services.
-
Choose Approved Enterprise Tools: Select tools that offer strong data privacy guarantees, do not train public models on proprietary code, and integrate cleanly with internal security controls.
-
Define Tiered Review Processes: Categorize tasks by risk level, ensuring high-risk code undergoes deeper scrutiny and senior architectural review.
-
Integrate CI/CD Guardrails: Embed automated linters, security scanners, and test suites directly into deployment pipelines to catch flawed code before it merges.
-
Train Engineering Teams: Educate developers on prompt engineering limitations, hallucination recognition, and critical evaluation techniques.
-
Measure Meaningful Metrics: Evaluate AI adoption success through metrics such as defect rates, review cycle times, and long-term maintainability rather than raw lines of code or generation speed.
For engineering leaders and business decision-makers, the goal is clear: use AI to support engineering judgment, not to replace accountability.
Call to Action
Navigating the balance between development velocity and software security requires deep technical expertise and structured governance. Whether you are building a new product from scratch, modernizing an existing application, or establishing safe governance for AI-assisted software development, our software development team can help you design robust architectures, implement secure coding practices, and maintain uncompromised software quality. Contact us today to discuss how to build maintainable, high-performance software with confidence.
